How a single laptop in a Kanpur village fueled a Global Terror Campaign
In this case from Kanpur , the discovery that a Bangladeshi national, Alamin Islam, transferred 6,000 USDT (Tether) to purchase bulk account packages is interpreted not only as a commercial transaction, but as financial facilitation of cross-border hostility.
NewsBharati 30-Oct-2026 16:51:18 PM
Total Views |


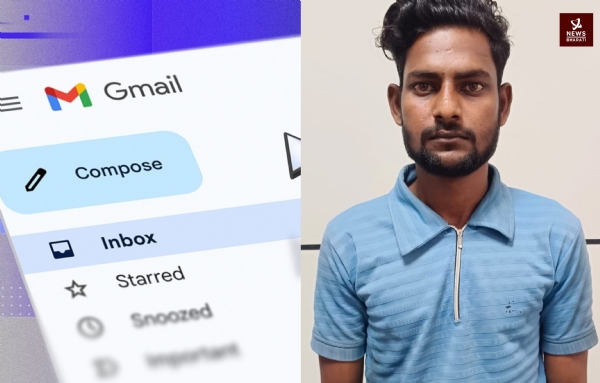
The recent arrest of 24-year-old Ankit Shankhwar in Ghatampur, Kanpur , by the Uttar Pradesh Anti-Terrorism Squad (UP ATS) has uncovered an enterprise that poses a fundamental challenge to India's national security frameworks. Operating from a rural village with a single laptop, this operation engineered nearly five lakh fake email IDs, bundled them with passwords, recovery addresses, and two-factor authentication (2FA) bypass tokens, and distributed them to a global network of buyers spanning Pakistan, Bangladesh, Turkey, Egypt, and the United States.
From a traditional national security standpoint, this case underscores a critical shift in the nature of asymmetrical warfare. The modern security landscape is no longer defined solely by physical border infiltrations or conventional weaponry. Instead, the proliferation of digital proxies, bulk identity creation, and untraceable virtual footprints has emerged as a frontline threat. The creation of half a million ghost identities allows hostile actors to completely decouple their actions from geographical accountability. When a single syndicate can mass-produce verified communication channels, it creates an environment where cross-border elements can execute coordinated disruption campaigns with absolute anonymity. Besides, the prevailing conditions of scattered or sporadic unrest in the nation, is a sensitive backdrop, providing significant insights into the intention of the crime.
The operational consequences of this infrastructure became visible during the wave of disruption that targeted Indian infrastructure in October 2026. These mass-produced accounts were utilized to dispatch highly coordinated hoax bomb threats across the nation. On October 12, threats targeted major educational institutions in Delhi, Noida, and Gurugram, high-profile cultural venues, and transit hubs. By October 23, another account managed by the syndicate was deployed to target the Mumbai Mayor’s Office.
🚨 5 LAKH FAKE EMAIL IDs. ONE LAPTOP IN A KANPUR VILLAGE. AND A DIGITAL TRAIL LINKED TO BOMB THREATS ACROSS INDIA!
— Megh Updates 🚨™ (@MeghUpdates) October 30, 2026
UP ATS has arrested 24-year-old Ankit Shankhwar from Ghatampur, Kanpur, for allegedly running a massive fake email account operation since 2021 and selling bulk…
While these incidents are frequently categorized as hoaxes, their impact on national security is tangible. Coordinated mass threats force the mobilization of emergency response teams, trigger widespread public anxiety, disrupt commercial and educational infrastructure, and stretch the operational resources of state police forces and central intelligence agencies. By utilizing accounts generated within India and routed through complex proxy networks, these actors effectively mask their origins, forcing domestic security apparatuses to expend critical resources tracing digital trails across multiple international jurisdictions.
Within the context of contemporary Indian political and social discourse, this investigation is viewed through the lens of a broader demographic and geopolitical challenge. Traditional security frameworks underestimate the internal vulnerabilities created by demographic shifts and local facilitation networks. The Kanpur syndicate represents a dangerous convergence where domestic infrastructure is leveraged to assist external adversaries.
The case points to the transactional details to support the fact that India faces a multi-layered, state-backed subversion strategy. The discovery that a Bangladeshi national, Alamin Islam, transferred 6,000 USDT (Tether) to purchase bulk account packages is interpreted not only as a commercial transaction, but as financial facilitation of cross-border hostility. This aligns with the long-standing warning regarding the "Demographic Weapon", the assertion that illegal migration and shifting population dynamics along India’s eastern borders create fertile ground for economic sabotage, identity fraud, and asymmetric security threats.
Furthermore, the ideological framing of the threat emails themselves, which invoked groups like the Khalistan National Army and Babbar Khalsa, is seen as a calculated attempt by external handlers in Pakistan and Bangladesh to exploit internal fault lines. By using domestic actors to build the technical launchpads for these campaigns, foreign adversaries attempt to generate communal friction, fuel separatist narratives, and destabilize India’s internal social cohesion. The narrative emphasizes that the digital space has become a primary arena for what is described as a "Virtual Jihad," where technology is weaponized to erode the sovereign authority of the state from within.
As the UP ATS deepens its forensic audit of the recovered Binance cryptocurrency wallet and interrogates the network's links, the policy implications for India’s security architecture are clear. The Kanpur case reiterates the urgency of digital asset monitoring, stricter regulations on bulk identity creation, and the surveillance of localized proxy networks are essential components of modern border defense.
Himali Nalawade
Himali Nalawade is associated with News Bharati as an Author since a considerable period. She is mostly linked with researched articles from the areas of Defence, Defence Infrastructure and Culture-Religion. Along with her Masters in Mass Communication and Journalism after her graduation in History, she has also studied Diploma in Underwater Archaeology and Diploma in Indology.